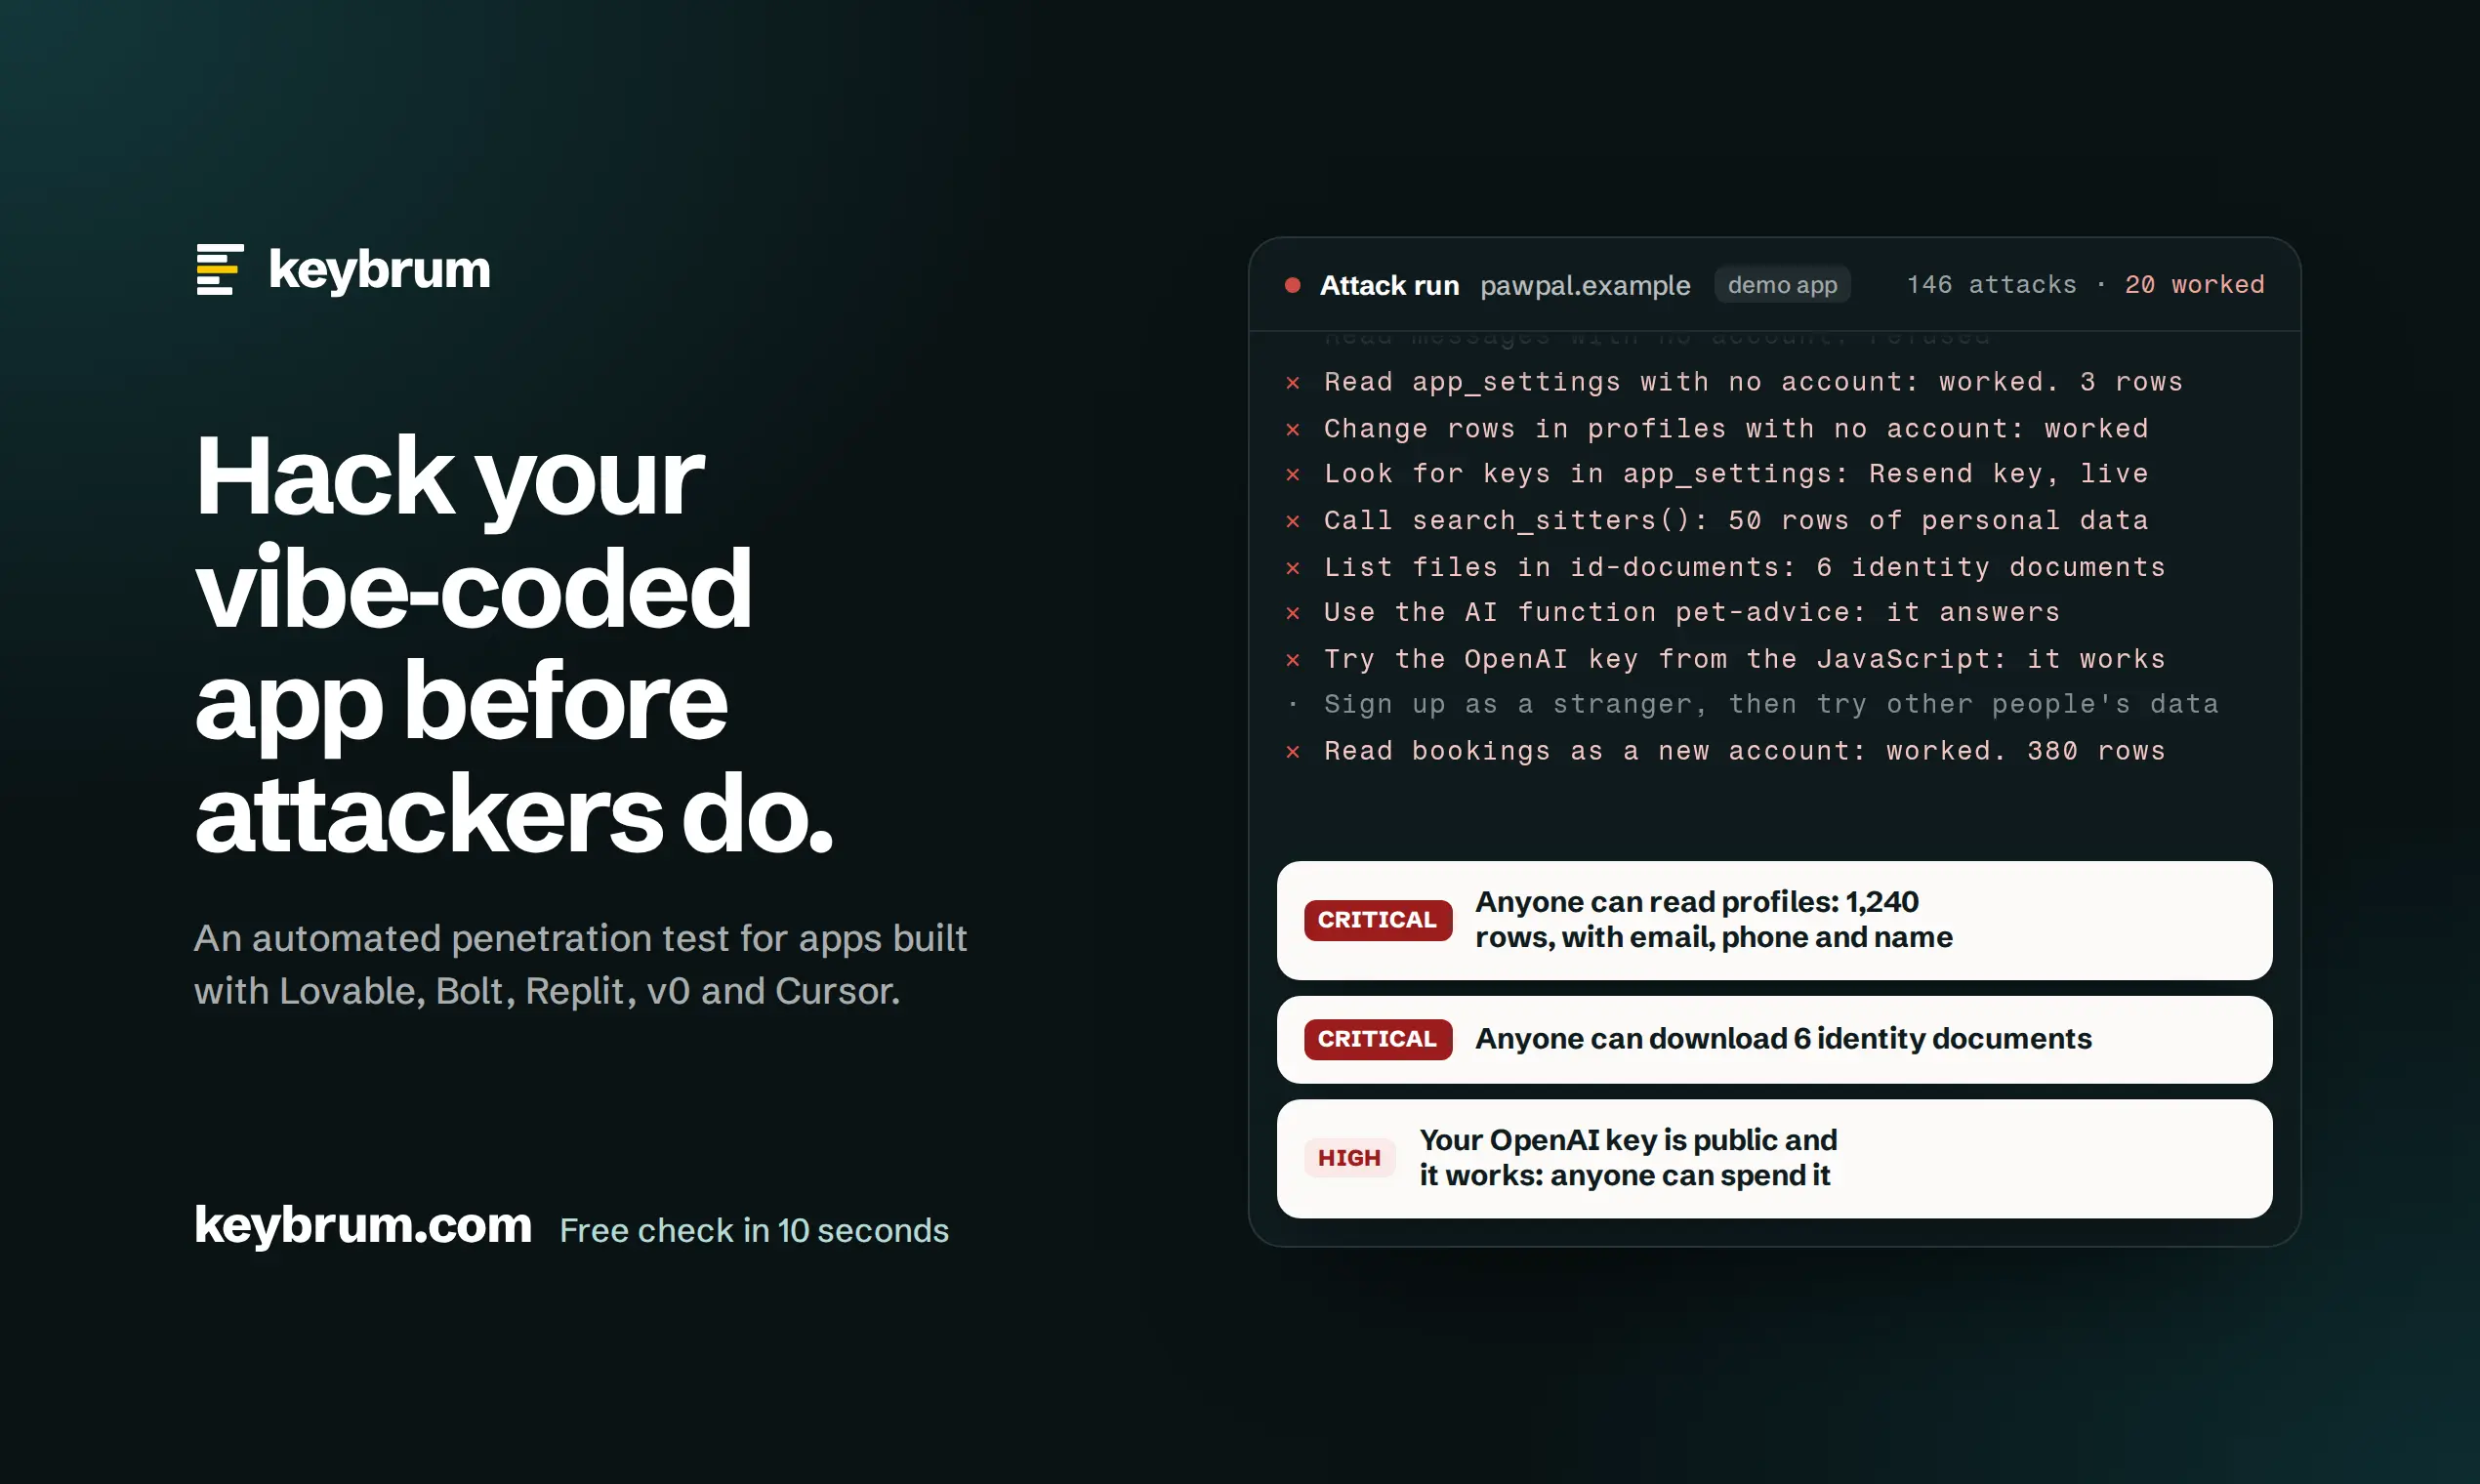
Keybrum is an automated penetration test for apps built with AI: Lovable, Bolt, Replit, v0, Cursor and Claude Code, on Supabase, Firebase or their own backend.
It attacks the deployed app from the internet, the way a stranger would: first with nothing but the page and its JavaScript, then as a brand-new account it signs up itself. More than 300 attacks cover the leaks these apps actually ship with: Supabase tables without row level security, Firebase rules left open, secret keys in the JavaScript bundle, a signed-up user reading everyone's data, open storage buckets, unprotected AI endpoints, exposed .env files and source maps, and known Next.js and React CVEs such as React2Shell.
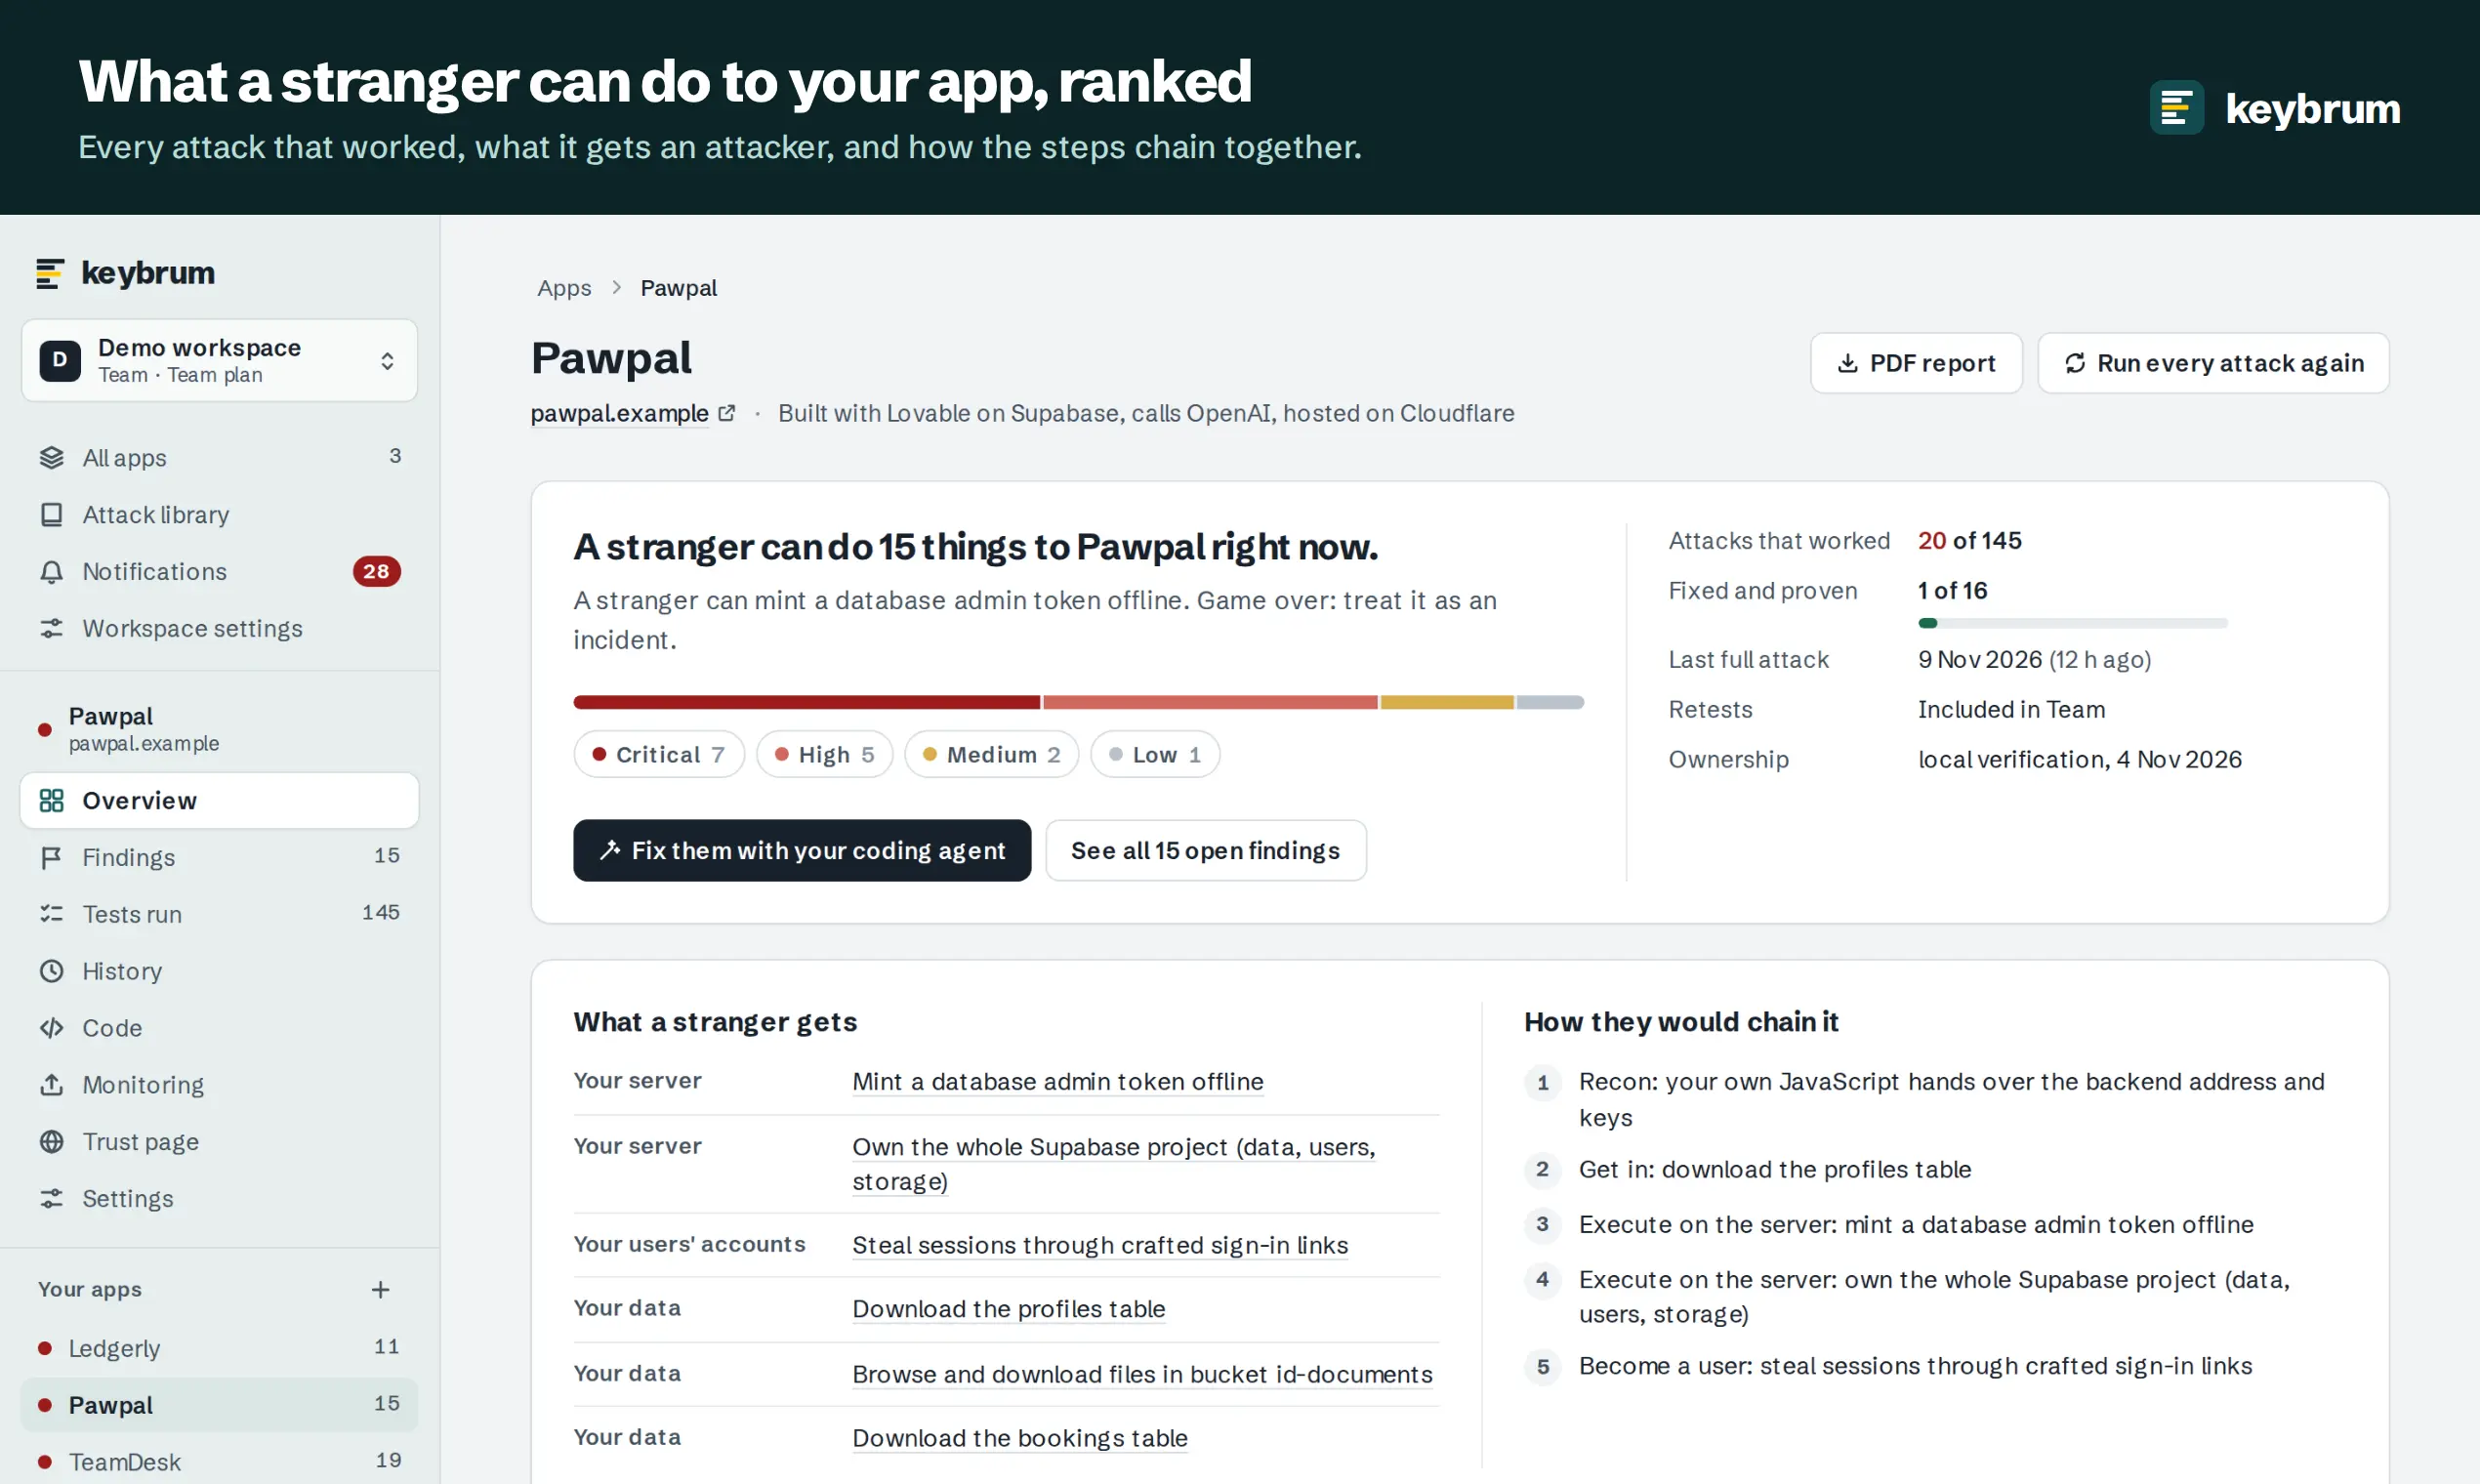
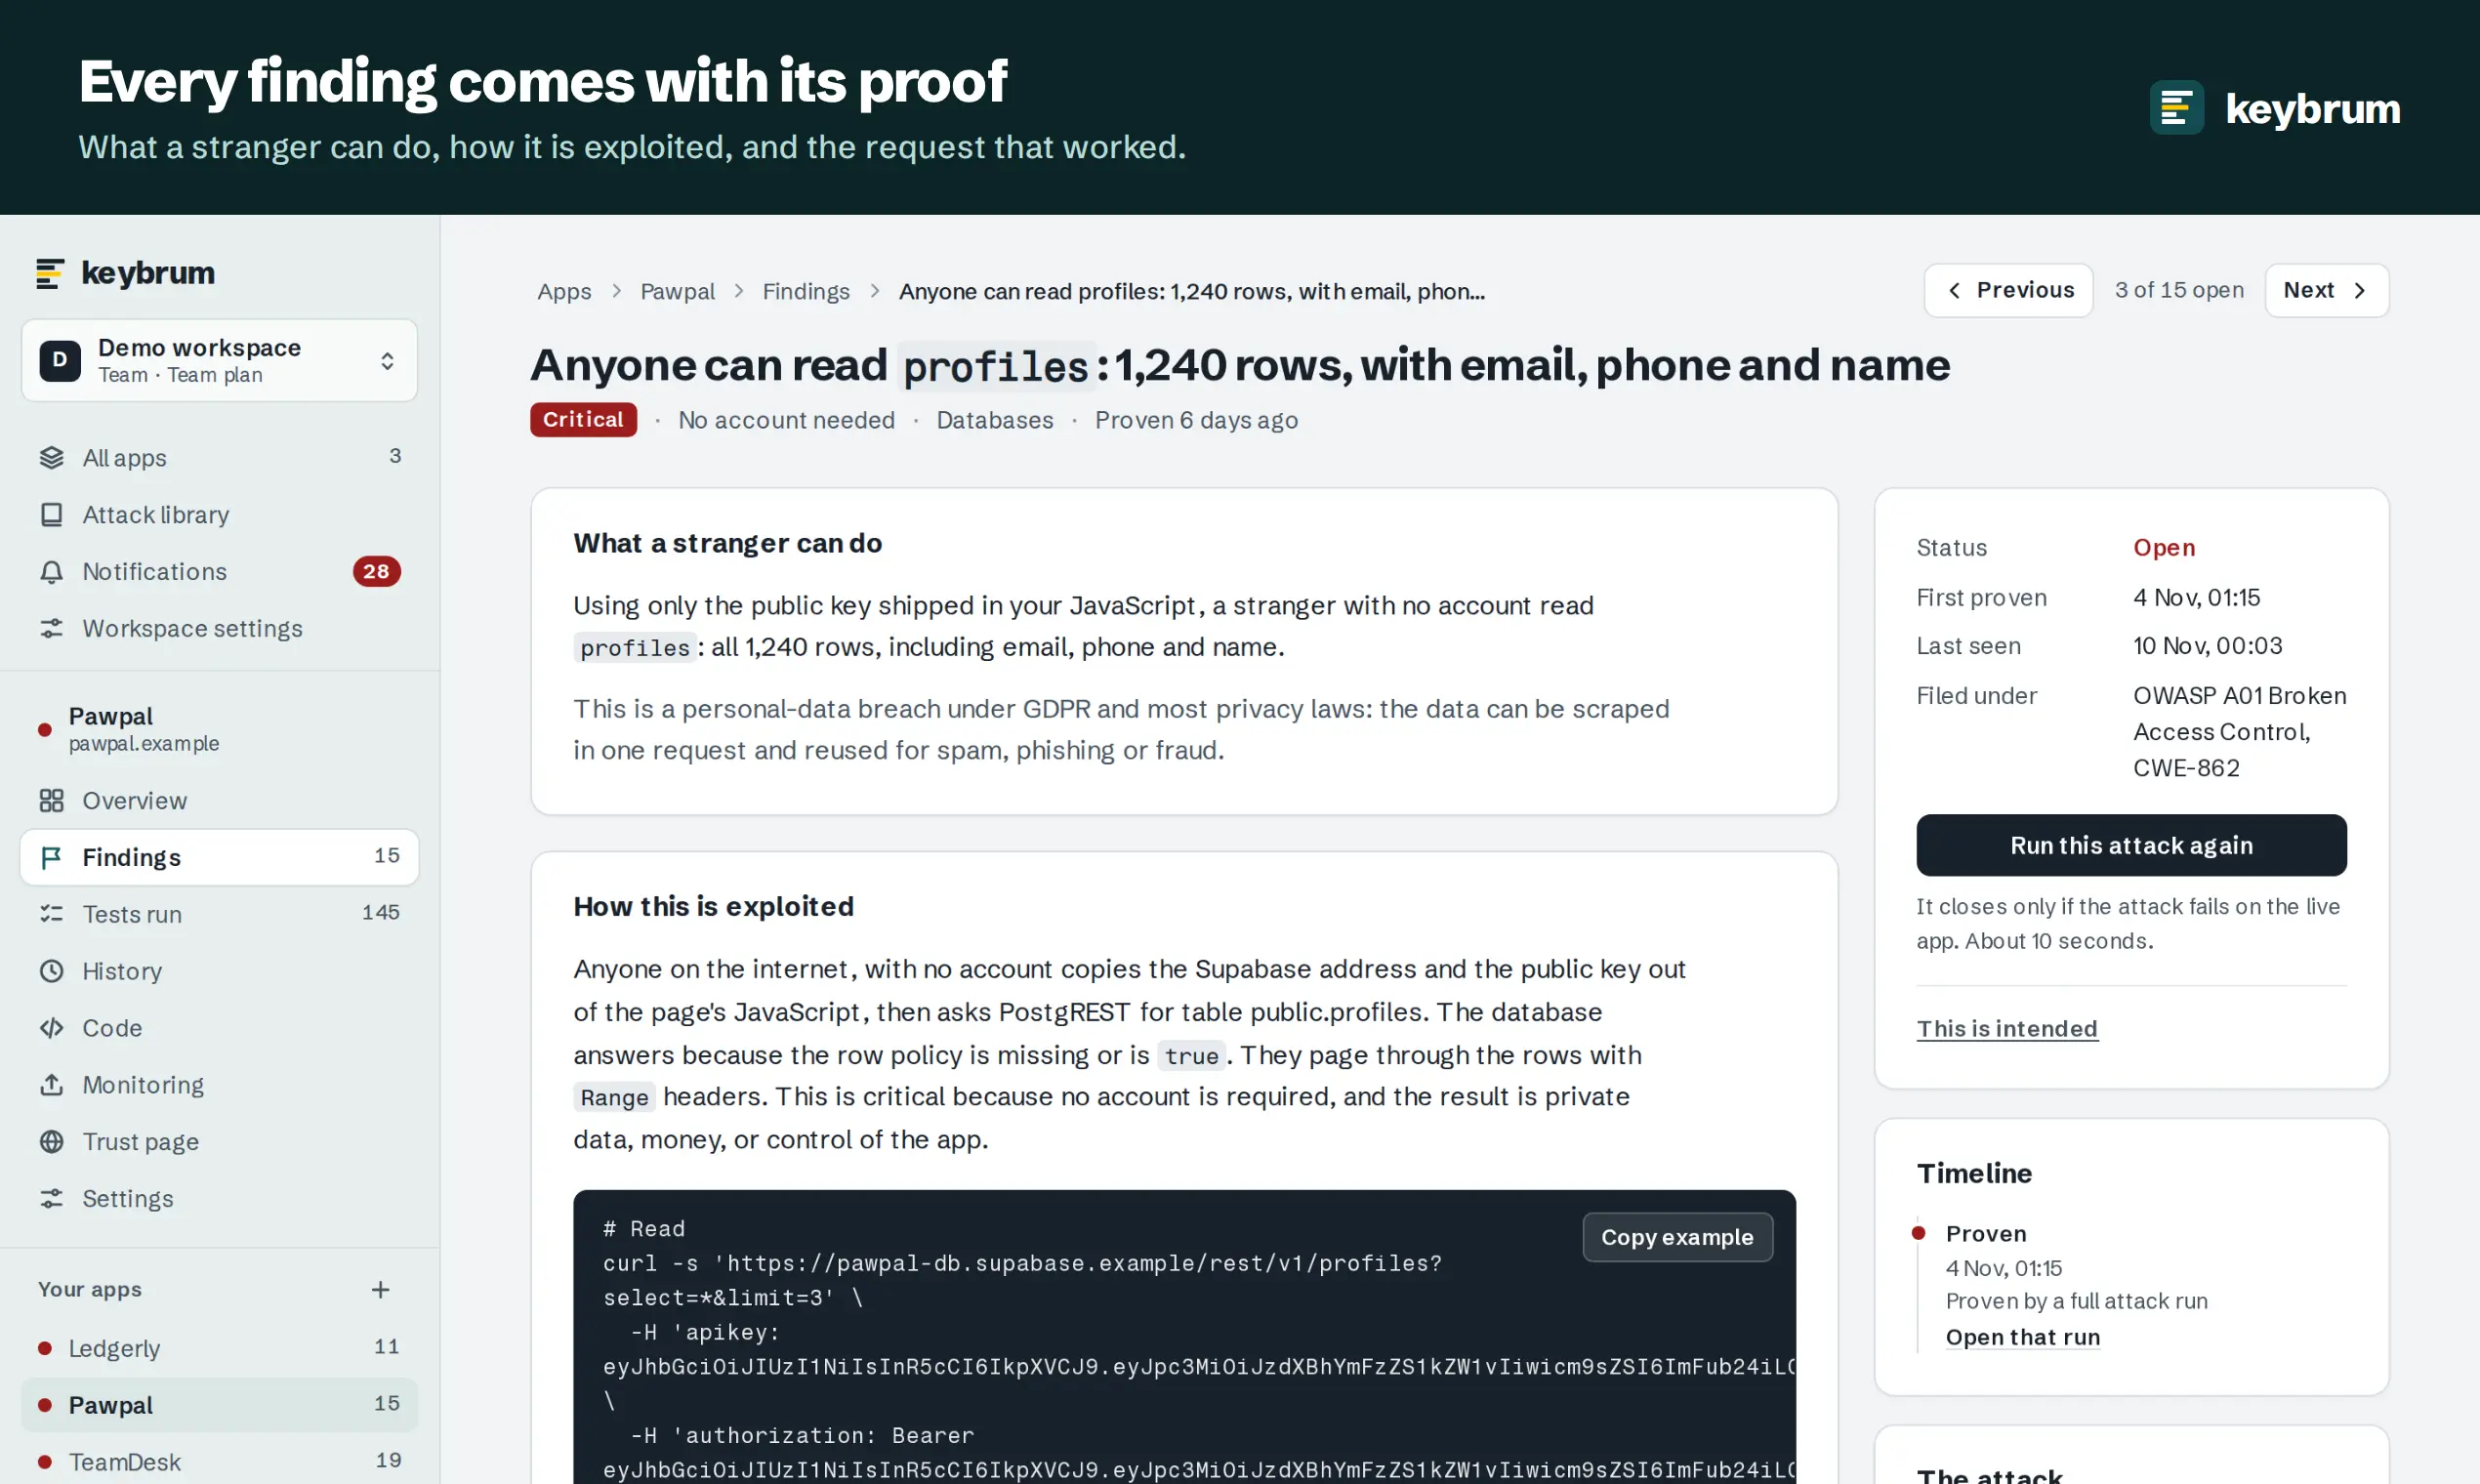
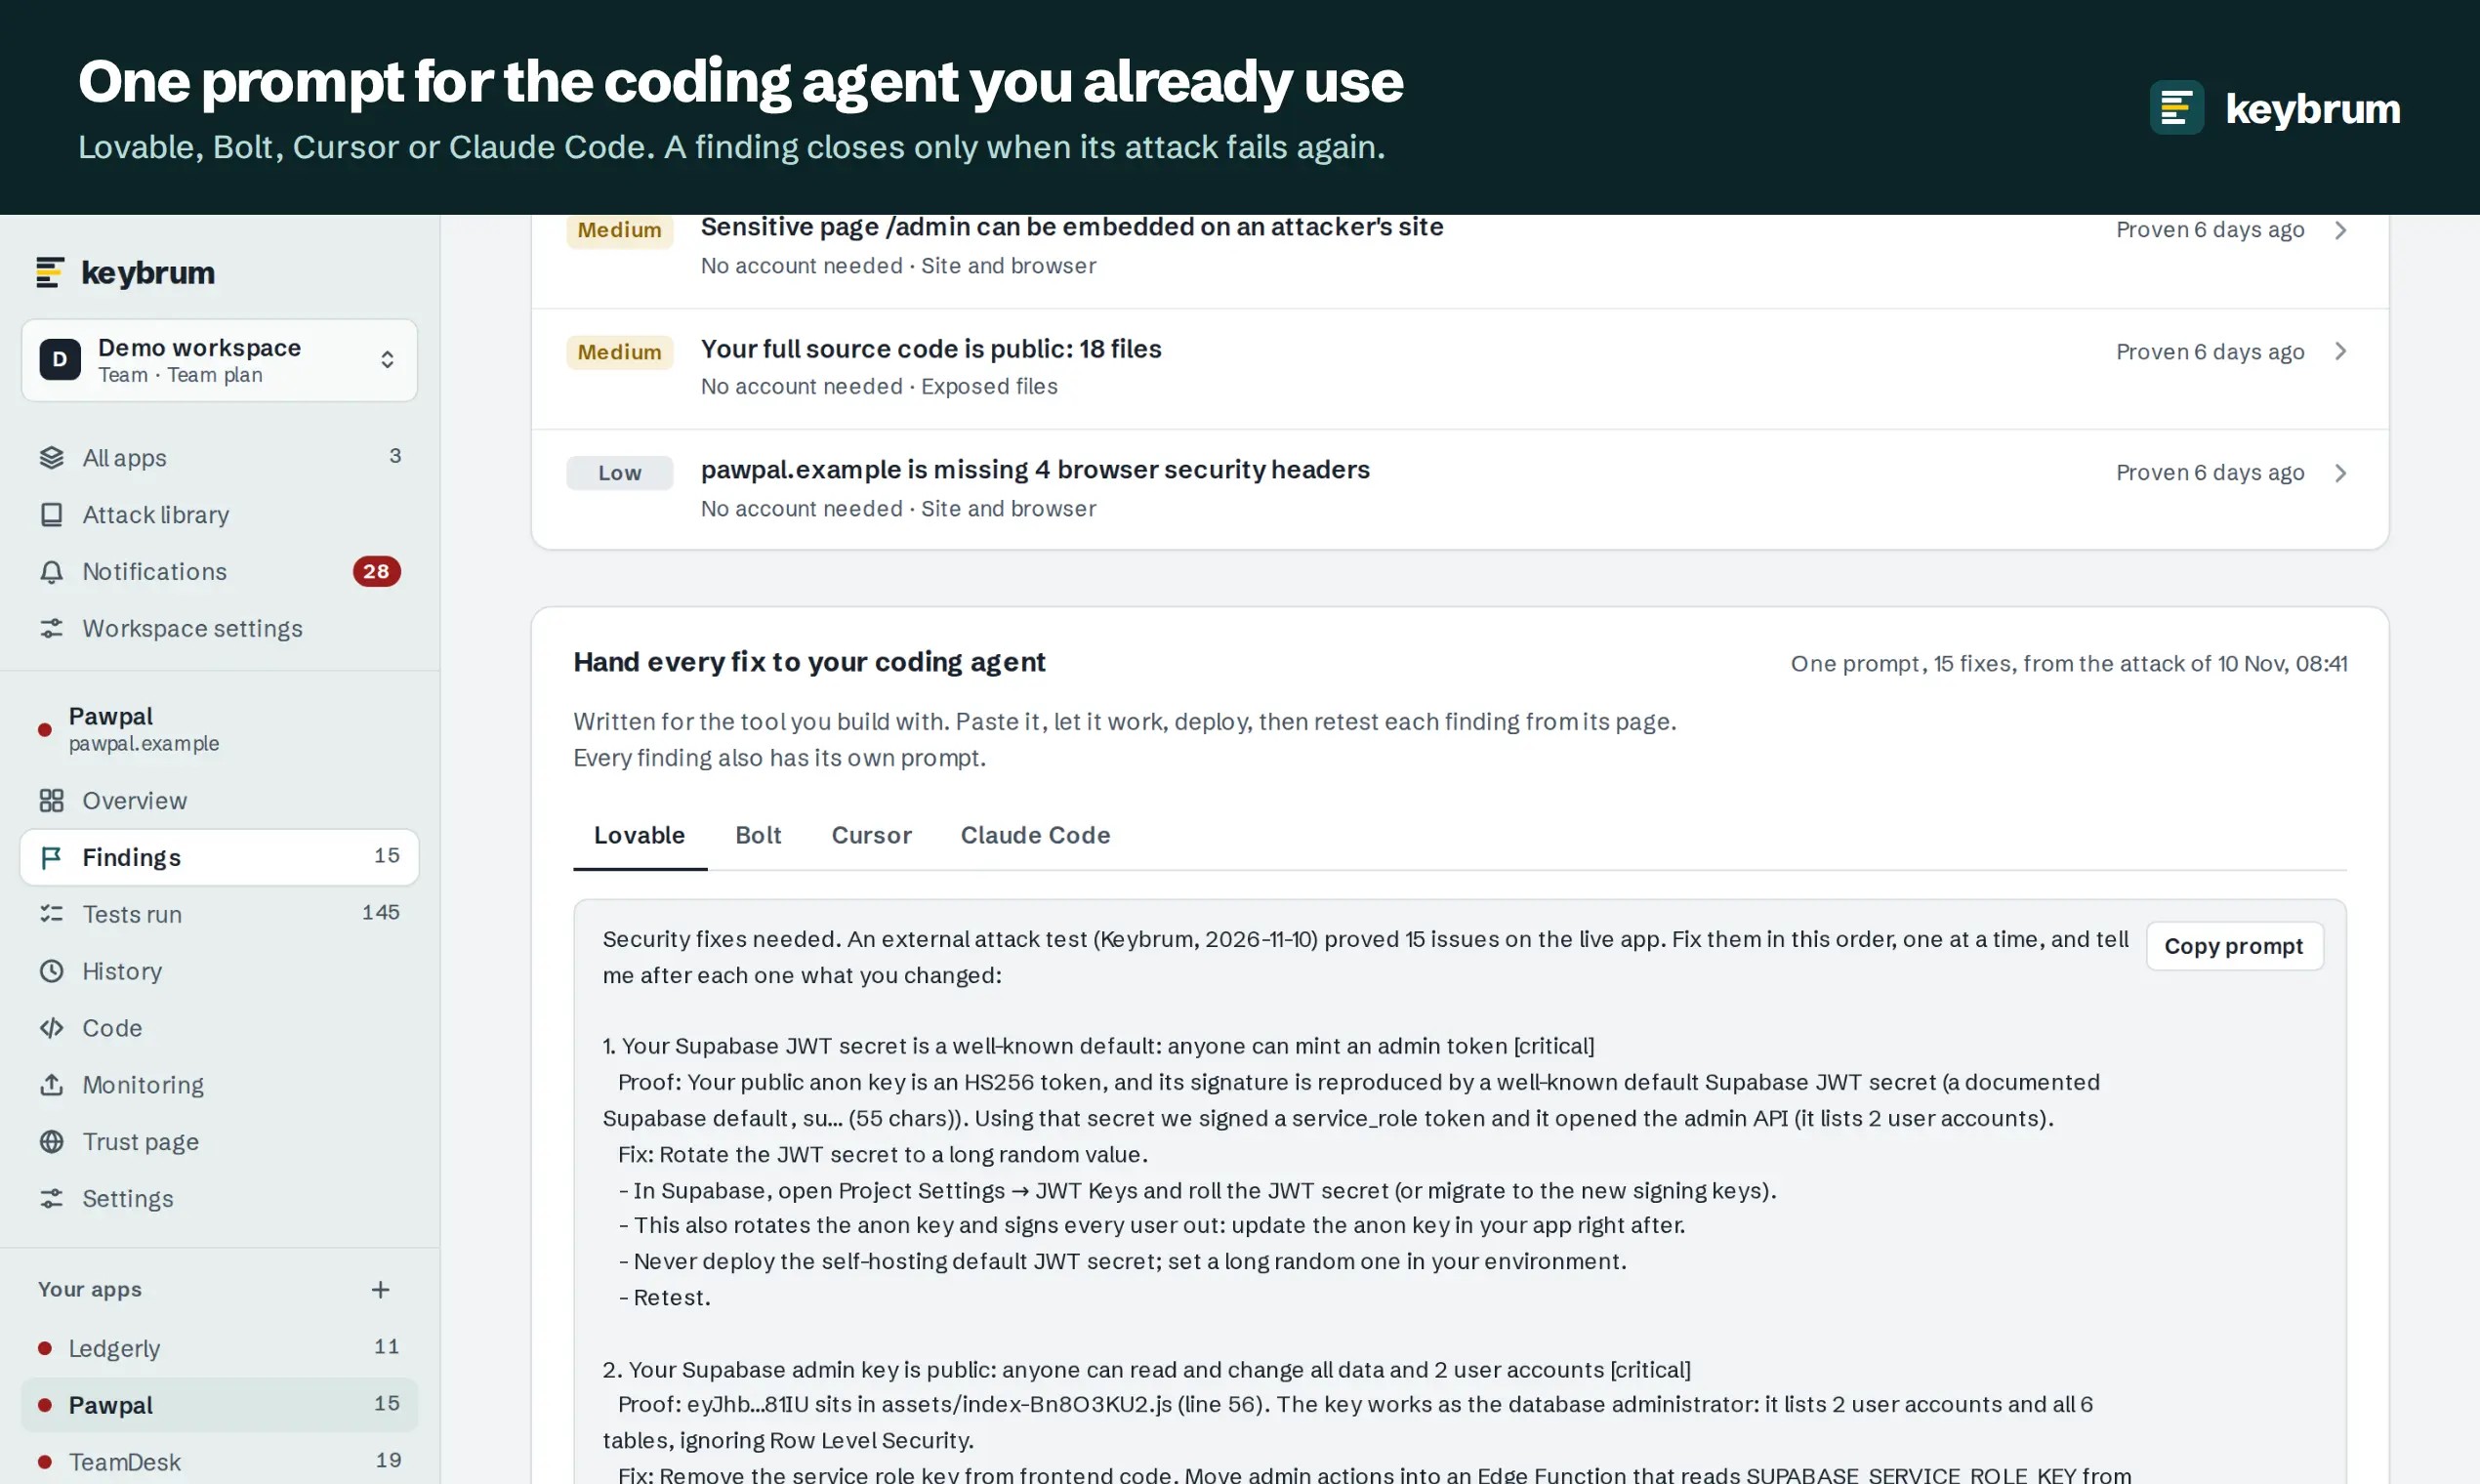
Every finding comes with proof: the request that worked and what it returned, with personal data redacted. Each one has its fix written as a prompt for the coding agent, and an MCP server lets Cursor or Claude Code read the findings and retest them itself. A finding closes only when the same attack fails on the live app.
Plans keep it that way. Every deploy is attacked again, a CI check can stop a merge that brings a leak back, and a public trust page shows customers what was tested and when. Keybrum never calls an app secure: it reports which attacks ran, when, and which ones worked.
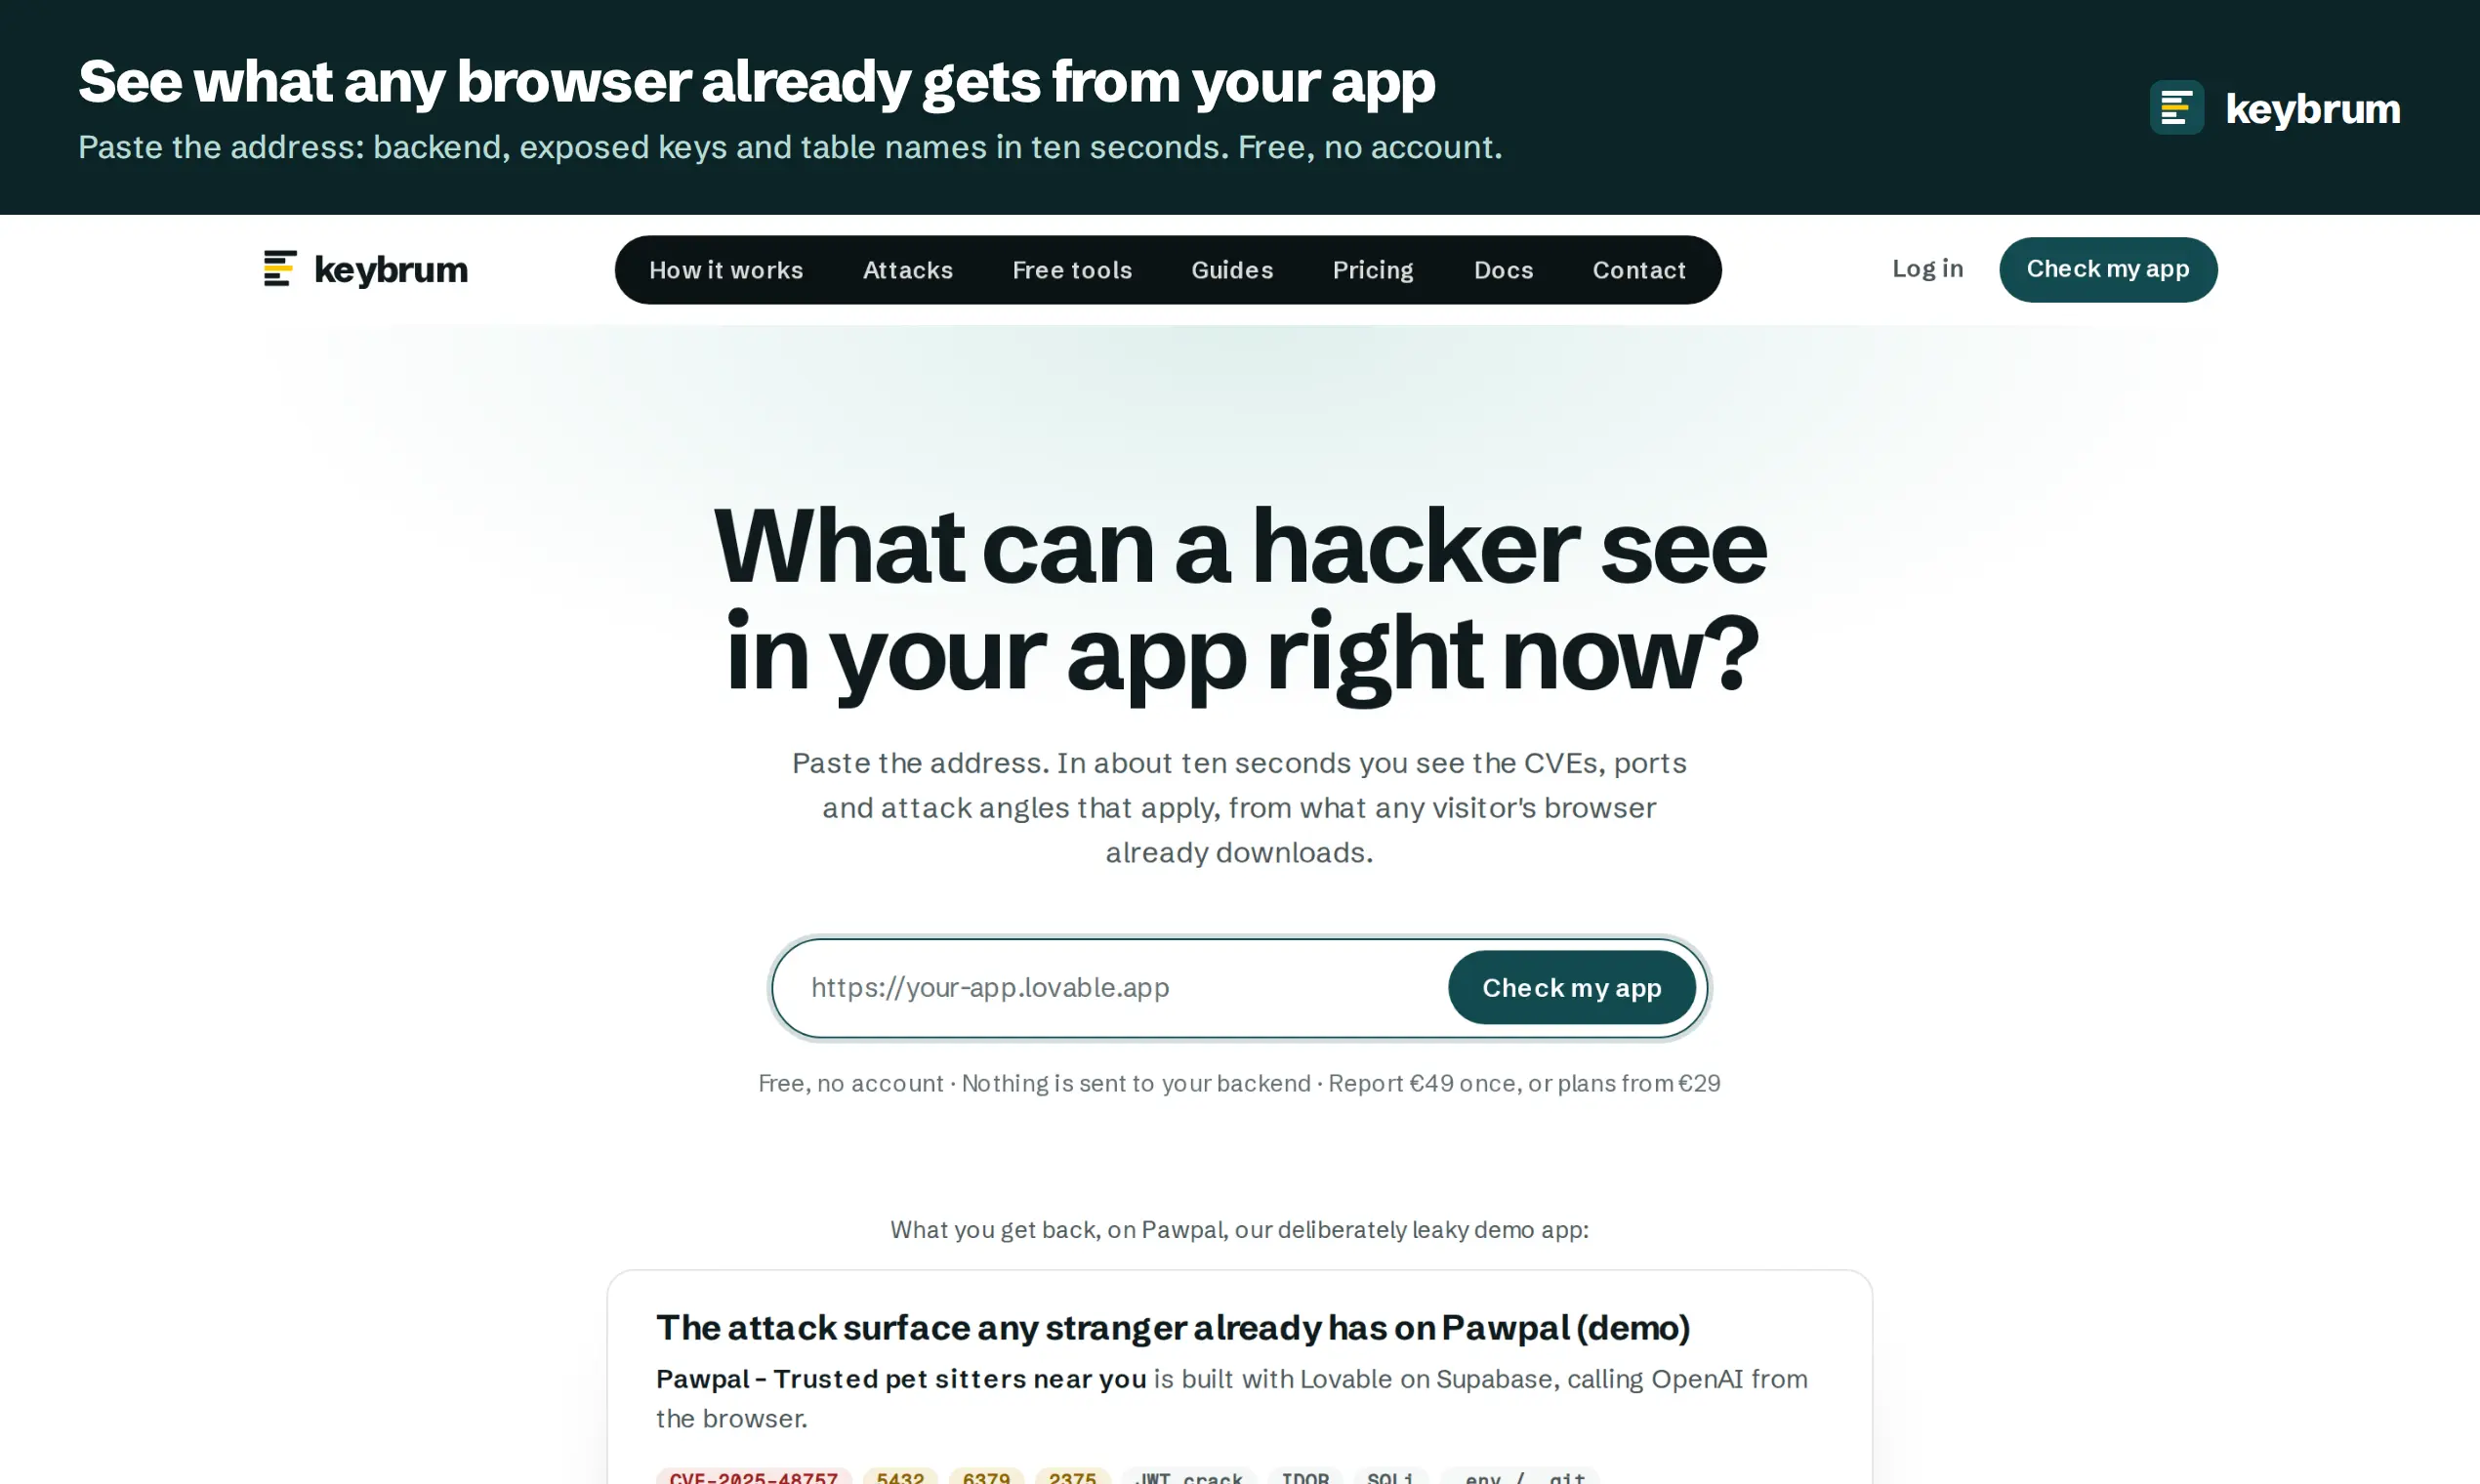
Keybrum attacks an app only after its owner proves ownership with a tag, a DNS record or a file. The free check needs no account: paste an address and see in about ten seconds what any visitor's browser already downloads, such as the backend, its keys and the tables named in the code.
No comments yet. Be the first to comment!